Passkeys offer strong phishing resistance, but their Achilles' heel lies in enrollment and recovery flows. Enterprises must secure these critical CIAM stages.
Enterprise security teams face new risks as attackers exploit passkey enrollment flows via vishing. Understand the evolving threat and harden your CIAM defenses.
A deep dive into the ZITADEL vulnerability cluster (CVE-2026-105209) exposing how passkey enrollment flaws enable cross-organization account takeovers. Learn how to protect your enterprise.
Enterprises face a critical gap in PQC readiness, focusing on data encryption while neglecting authentication infrastructure. Start testing certificate ecosystems now.
Enterprises face an urgent need for crypto-agility as the quantum threat looms. This article explores why PQC readiness is fundamentally a Certificate Lifecycle Management (CLM) challenge.
As passkeys become default, enterprises face new social engineering threats targeting enrollment and recovery flows. Secure your CIAM against these evolving attack vectors.
Enterprise security leaders must recognize that while passkeys are phishing-resistant, social engineering tactics exploit human elements in their deployment. Learn how to secure your CIAM.
As passkeys become default, new social engineering tactics emerge. Enterprises must secure their CIAM against sophisticated phishing and identity hijacking attempts.
Passkeys offer strong phishing resistance, but new social engineering tactics are exploiting their adoption. Learn how enterprises can defend against these evolving threats.
Cloudflare's new public CA and Merkle Tree Certificates mark a significant leap in post-quantum PKI. Enterprises must understand its implications for cryptographic agility.
Cloudflare's new public CA and Merkle Tree Certificates (MTCs) represent a significant step toward post-quantum cryptography. Learn what this means for enterprise PKI.
Enterprises face a new challenge with passkeys: social engineering attacks exploiting user trust to bypass phishing-resistant authentication methods. Learn how to defend against this evolving threat.
Despite enhanced security, passkeys are becoming a new target for social engineering, leading to enterprise cloud account compromises. Learn how to defend against these evolving threats.
Attackers are using sophisticated social engineering tactics to bypass passkey security, exploiting human trust to compromise enterprise cloud accounts. Learn to defend your organization.
Passkeys offer strong phishing resistance, but social engineering exploits human trust. Learn how attackers are using fake passkey prompts for account takeover.
Attackers are weaponizing passkey adoption against enterprises, using social engineering to hijack Microsoft 365 accounts and exfiltrate data. Learn how to defend against this evolving threat.
Attackers exploit passkey and MFA enrollment flows with social engineering. Enterprises must understand these evolving threats to secure identities and cloud data.
Enterprise security teams face new identity threats as attackers weaponize passkey adoption through sophisticated social engineering tactics and AiTM phishing.
Passkey-themed social engineering campaigns are circumventing phishing resistance. Learn how attackers establish persistence and exfiltrate data, and what enterprises must do to secure their cloud identities.
Enterprise security teams must defend against sophisticated social engineering attacks exploiting passkey enrollment and recovery processes, bypassing strong authentication.
Explores how threat actors are exploiting the enterprise transition to passkeys through social engineering, turning a security upgrade into a new attack vector for cloud identity compromise.
Explore how passkey-themed social engineering attacks are bypassing traditional MFA, leading to M365 data theft and cloud compromise. Learn to defend your enterprise.
Passkey adoption is surging, yet new research reveals 39 attack methods bypassing phishing resistance without breaking FIDO2 crypto. Enterprises must secure the ecosystem, not just the protocol.
Federal agencies now require Cryptographic Bills of Materials (CBOMs). Learn what CBOMs are, why they are critical for PQC migration, and how enterprises can prepare.
Discover the critical distinction between FIDO2 protocol strength and passkey ecosystem vulnerabilities. This article explores emergent attack vectors and strategies for enterprise-grade passkey security.
Passkeys promise phishing resistance, yet new research reveals a growing attack surface from implementation flaws and endpoint compromises. Enterprises must secure the entire authentication ecosystem.
Enterprise passkey adoption faces new security challenges. Recent research highlights architectural flaws and exploitation scenarios beyond the FIDO2 protocol, requiring a reassessment of enterprise passkey security strategies.
Browser trust deadlines are providing an early, urgent test of cryptographic agility. Enterprises must assess their PQC readiness to avoid service disruptions.
Explore the evolving threat landscape for passkeys, analyzing recent "Pass-the-Passkey" attacks and outlining enterprise strategies to bolster passkey security and governance.
Enterprise security leaders must navigate the complexities of hybrid post-quantum TLS and understand where classical certificates still dominate the authentication landscape.
The IETF is prioritizing post-quantum authentication deployment, highlighting critical gaps beyond protocol standardization. Enterprises must focus on practical implementation challenges.
Explore iAuthFlow v2, a $10K phishing kit enabling persistent access via rogue passkeys. Learn how this browser-in-the-middle attack bypasses password resets and session revocations, and what enterprises must do to defend against this evolving threat to identity security.
Passkeys promise phishing resistance, but new attacks demonstrate how advanced kits exploit implementation flaws and synchronisation, demanding renewed enterprise vigilance.
Passkeys promise phishing resistance, but recent research exposes critical vulnerabilities through endpoint compromise. Enterprises must understand passkey security limitations.
Passkeys promise phishing resistance, but recent research reveals critical vulnerabilities when endpoints are compromised. Learn how these attacks redefine enterprise identity security.
Passkeys offer strong phishing resistance, but new research highlights vulnerabilities related to human behavior and shared devices. Enterprises must understand these risks.
Passkeys offer phishing resistance but introduce novel attack vectors. Enterprises must understand evolving threats like replay and abuse to secure modern identity systems.
A Cornell study highlights passkey vulnerabilities for abuse survivors. Enterprises must understand these risks and implement safeguards beyond technical phishing resistance.
Enterprise security leaders must converge PKI modernization, Post-Quantum Cryptography (PQC) migration, and automated certificate management to meet evolving threats and regulatory demands. Learn why these are no longer separate initiatives.
The accelerating PQC timeline demands enterprises rethink PKI. This article explores the challenges of hybrid certificate migration and operational agility.
Explore the recently discovered "Pass-ta-key" attacks, dissecting their mechanisms and impact on enterprise security. Understand the critical distinction between protocol flaws and implementation vulnerabilities in passkey ecosystems.
Explore the nuances of recent passkey attacks, focusing on implementation vulnerabilities rather than cryptographic weaknesses. Learn how to secure enterprise passkey deployments.
Analyzes the "Pass-ta-key" attacks, revealing how malware exploits synced passkeys and emphasizing the need for robust enterprise security practices beyond FIDO2 cryptography.
Palo Alto Networks researchers have uncovered "Pass-ta-key" attacks, highlighting how malware can compromise synced passkeys and emphasizing the need for robust enterprise security.
Explore the "Pass-ta-key" attacks and their implications for enterprise passkey adoption. Balance security with user experience in a post-password world.
Palo Alto Networks' "Pass-ta-key" attacks reveal critical implementation flaws in passkey systems, emphasizing the need for robust endpoint security and careful integration to prevent account hijackings. Learn how enterprises can defend against this novel threat.
Post-quantum cryptography introduces larger signature sizes, challenging existing TLS handshake limits. Learn how this impacts enterprise PKI and what to do.
Passkeys enhance security, but recent exploits highlight critical vulnerabilities in implementation, from malware hijacking to vishing. Enterprises must address these new attack vectors.
New research exposes vulnerabilities in Google-synced passkeys, highlighting the critical role of endpoint security in passwordless authentication. Enterprises must re-evaluate trust models.
Explore the emerging attack surfaces of passkeys, analyzing how novel techniques like "Pass-ta-key" and enrollment vishing exploit implementation gaps, not crypto flaws.
Cloudflare has enabled post-quantum authentication to origins, marking a significant step in PQC migration. Learn what this means for enterprise security.
A vendor-neutral buyer's guide to PKI management. Compare discovery, automation, protocol support, crypto-agility and pricing models before you commit.
Cloud KMS platforms now offer ML-DSA and SLH-DSA signing keys. What quantum-safe signatures change for code signing, document integrity and enterprise PKI.
Microsoft rolls out hybrid post-quantum key exchange to Windows TLS, impacting enterprise security teams. This article details the update and its implications.
How we migrated a global enterprise from fragile on-prem PKI to an automated, crypto-agile, quantum-ready PKIaaS built for 90-day TLS and post-quantum threats.
A new vishing campaign targets Microsoft 365 users by exploiting the passkey enrollment process, highlighting critical vulnerabilities in user education and.
Microsoft’s accelerated 2029 PQC timeline underscores the urgent need for enterprise PKI and IAM teams to prioritize quantum-safe migration strategies.
Microsoft has accelerated its Post-Quantum Cryptography (PQC) migration timeline to 2029. This analysis explores the implications for enterprise security.
Singapore's national digital identity, Singpass, integrates passkeys to enhance security and user experience, directly countering rising phishing attacks.
Microsoft moved its post-quantum cryptography target to 2029. See what the compressed timeline means for enterprise PKI, TLS and crypto-agility planning.
Microsoft has accelerated its PQC rollout across Windows and Azure. Learn which cryptographic dependencies enterprises should inventory and migrate first.
Explore the growing pressure for enterprises to adopt passkeys, their benefits in phishing resistance, and the critical governance considerations for IAM teams.
The White House has drastically shortened deadlines for federal agencies to adopt post-quantum cryptography (PQC), impacting enterprise security planning.
The White House issues new executive order shortening deadlines for federal agencies to transition to Post-Quantum Cryptography (PQC), impacting enterprise.
The White House has issued a new executive order to accelerate the transition to post-quantum cryptography. Learn what enterprise security teams need to do now.
EO 14412 accelerates the US federal PQC deadline. Here's the enterprise PKI checklist — crypto inventory, hybrid certs and migration steps — to get ready now.
The White House issues executive orders accelerating the federal government's transition to Post-Quantum Cryptography. Enterprises must map their PKI now.
The White House mandates a federal transition to post-quantum cryptography. See how enterprises should prepare with PKI modernisation and crypto-agility.
ETRI's new QuantumPKI Studio aids enterprises in validating post-quantum and hybrid certificates, streamlining the critical migration to quantum-resistant PKI.
A new FIDO Alliance and HID study reveals a significant gap between perceived and actual identity security, highlighting risks from fragmented management.
NIST proposes a dual-stack model for Personal Identity Verification (PIV) standards, integrating post-quantum cryptography while maintaining compatibility.
Explore the growing momentum of passkeys for enterprise authentication, analyzing their security benefits, CIAM integration challenges, and strategic rollout.
NIST has finalized post-quantum signature standards. Here is what they change for enterprise PKI, code signing, and authentication — and how to prepare.
A practical guide for enterprises planning to retire Microsoft Active Directory Certificate Services and move to a modern, automated, crypto-agile PKI.
Lack of certificate visibility is a major enterprise blind spot, causing outages and security gaps. Learn how PKI modernization and automation close it.
A new phishing technique, VaultJacking, demonstrates how capturing a single Google Password Manager PIN can expose an entire vault of passkeys and passwords.
Explore the Tycoon 2FA AiTM phishing kit, its ability to bypass MFA on Microsoft 365/Entra ID and Google Workspace, and crucial enterprise defense strategies.
Strategic guidance for CISOs and security architects on migrating enterprise PKI to post-quantum cryptography (PQC) ahead of harvest-now-decrypt-later risk.
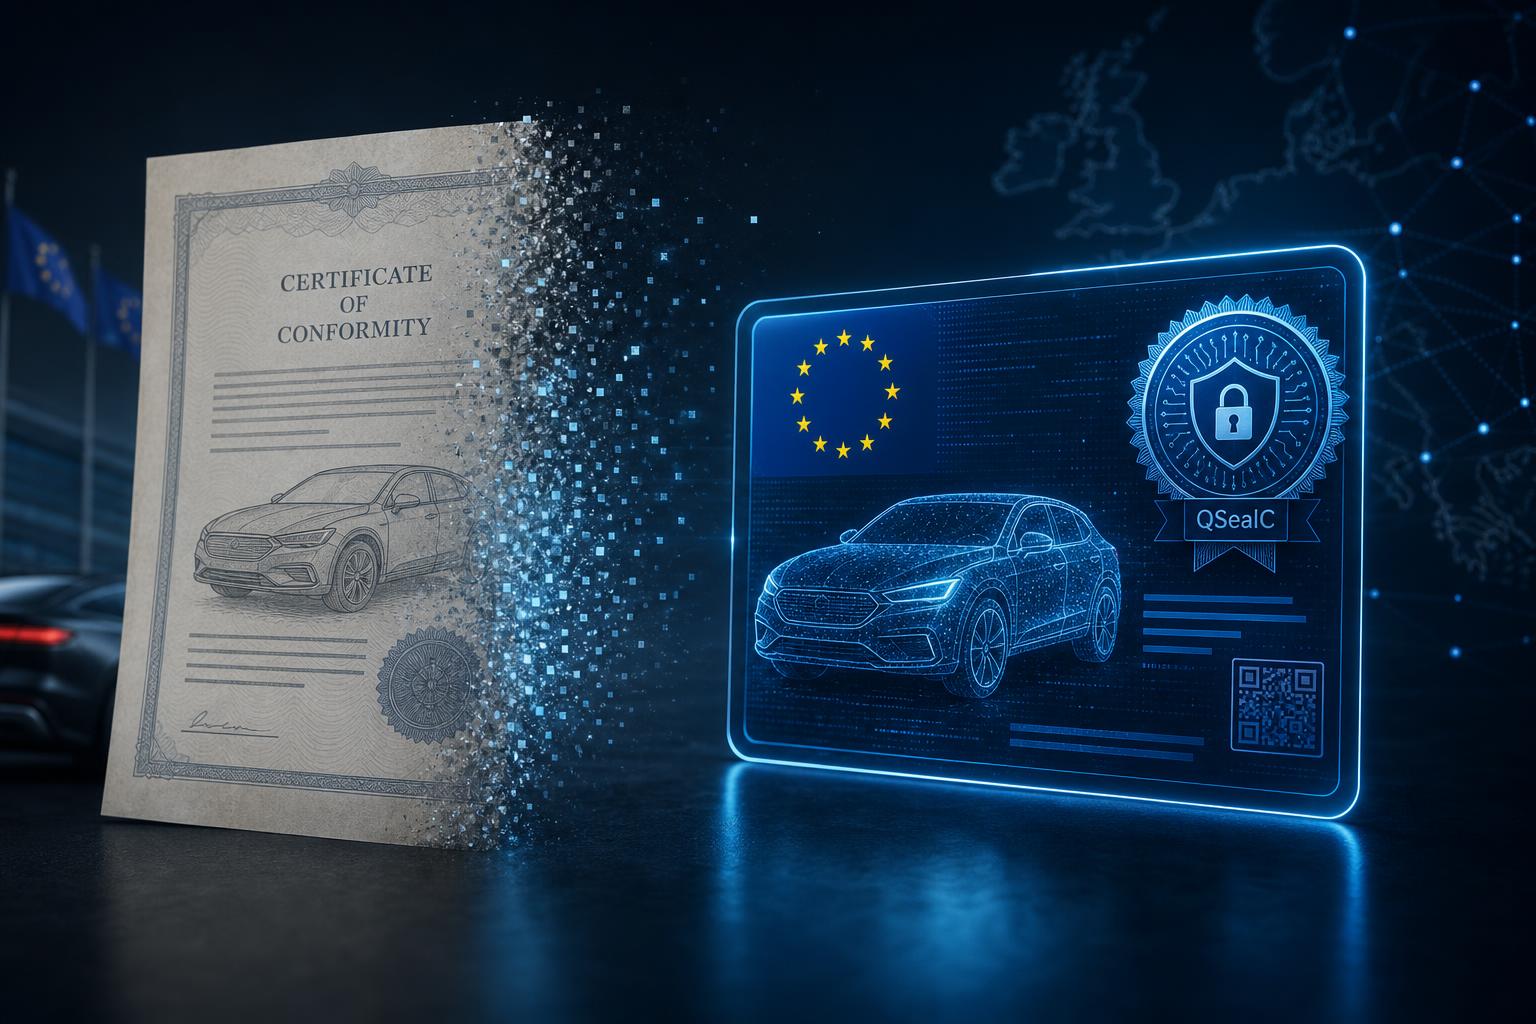
Prepare for the EU's July 2026 mandate replacing the paper Certificate of Conformity (CoC) with Initial Vehicle Information (IVI) XML files secured by QSealC.
CIAM vs IAM compared in plain English: scale, branding, auth, data, cost. When to use Entra ID for workforce vs Azure AD B2C / Entra External ID for customers.
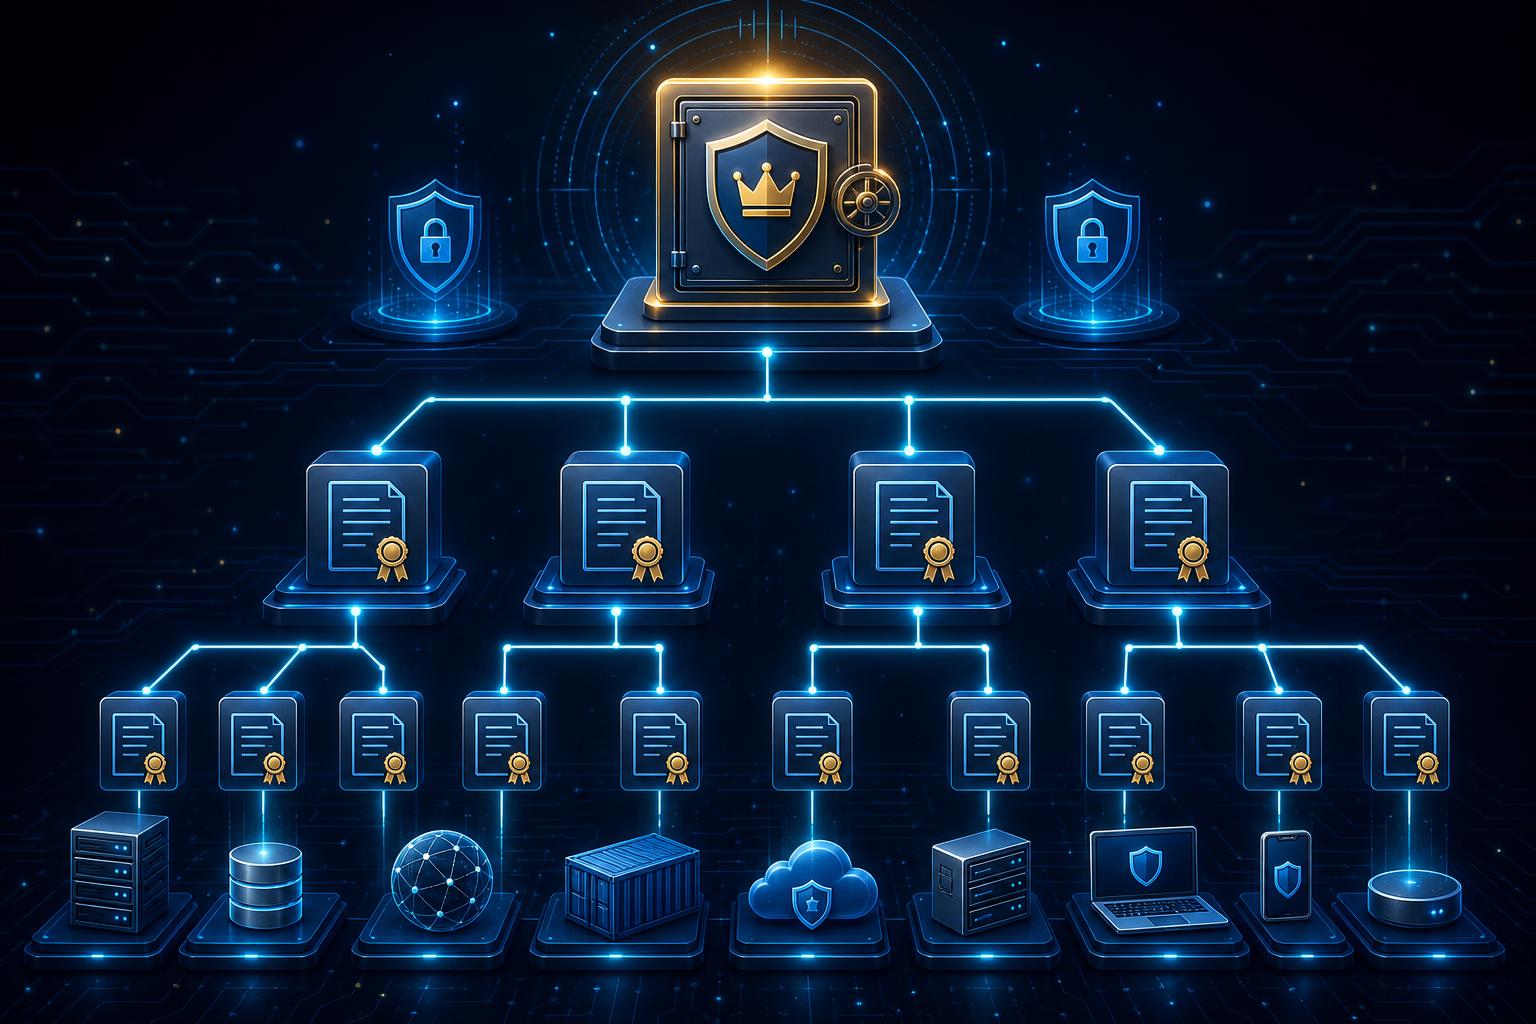
What is PKI? Public Key Infrastructure explained simply — how digital certificates, certificate authorities, and public/private keys secure the enterprise.
 Identity & Access